

Hackers compromised a widely used Injective software package in a supply chain attack with malware designed to steal crypto wallet private keys, adding to a growing attack vector involving attackers using legitimate platforms to deliver malicious payloads.
Security firm Socket discovered on Thursday that a popular npm (node package manager) package with around 50,000 weekly downloads used for building on the Injective blockchain was maliciously modified to steal wallet private keys and seed phrases.
The large number of downloads makes the incident “significant for developers and applications that handle Injective wallet workflows,” Socket researchers said. The malicious code has since been removed.
The software supply chain attack is a relatively new attack vector in which hackers don’t target a blockchain’s cryptography or smart contracts directly, but instead compromise trusted developer tools used to build wallets, exchanges and apps.
Injective is an interoperable layer 1 designed for DeFi applications. Its usage has dwindled over the past two years, with total value locked shrinking by 88% to current levels of $8.2 million from its $71 million peak in mid-2024, according to DefiLlama.
Secretly copying private keys and phrases
Version 1.20.21 of the @injectivelabs/sdk-ts npm package was modified through a compromised developer GitHub account, with suspicious commits beginning June 8. It was also pinned across 17 other packages in the Injective Labs npm scope, “exposing users who may not have installed the SDK [software development kit] directly,” Socket said.
“The malicious release hooks wallet key-derivation functions, records private keys and mnemonics, and exfiltrates them through fake telemetry,” Socket explained.
The malicious code hooked into normal functions used to generate wallet keys, and whenever a developer’s app used these functions, it secretly copied the seed phrase or private key. The compromised data was then encoded and sent to a web address that looked like a legitimate Injective network server.
“Any keys or mnemonics passed through affected packages should be treated as compromised,” Socket added.
Related: ‘TrapDoor’ malware targets crypto dev tools in supply chain attack
Socket reported that the developer whose account was infiltrated quickly detected the compromise, but the malware had been downloaded more than 300 times, and “the campaign itself isn’t yet fully contained.”
Injective CEO Eric Chen said, “it’s already fixed, and the affected versions on npm are already deprecated.” No funds on the network are at risk, he added, and Socket did not specify whether any funds were stolen in the incident.
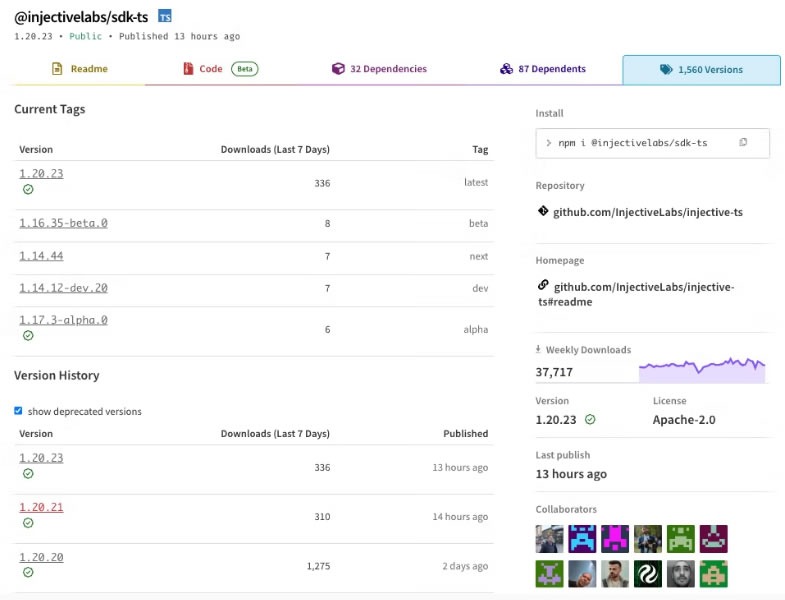
The compromised npm package was downloaded 310 times. Source: Socket
Wallet compromises most costly this year
The Security Alliance (SEAL) said in its second-quarter threat report that attackers are increasingly using legitimate platforms like GitHub, npm and Google to deliver payloads.
“In some cases, compromised systems are being used to push malicious code directly into a company’s own GitHub repositories, turning a single compromise into a distribution channel for the next one.”
SEAL added that the malware itself has also gotten more comprehensive, “with cross-platform payloads, including a rise in macOS-specific campaigns, that combine infostealers, RATs (remote access trojans) and backdoor capabilities in a single package.”
A similar supply chain attack hit Axios npm releases in March, while a malware campaign called TrapDoor was discovered in May targeting crypto, DeFi, AI and security developers.
GitHub itself was exploited on May 20 when it reported unauthorized access to its internal repositories following the compromise of an employee’s device.
Wallet compromises were the most costly attack vector in the first half of 2026, with $444 million stolen across 33 incidents, CertiK reported Monday.
Features: Bitcoin’s quantum dilemma: Bigger blocks or STARK proofs?